Federal Logging Plans Require Continuous Proof of Capability Over Static Documentation
Modern federal logging mandates demand a transition from static compliance documentation toward automated, self-validating telemetry systems. This shift ensures that data collection remains actionable, reliable, and fundamentally prepared for real-time security investigations.
Compliance as a Derivative of Engineering
Federal agencies are currently navigating the transition from the mandate of OMB M-26-14 to the tactical reality of CISA's Logging Reference Architecture (LRA). For years, federal IT leaders treated logging as a checkbox exercise. The operational rhythm involved collecting logs, dumping them into a repository, and asserting that the boxes were checked for the annual audit. This approach creates a dangerous illusion of security. An agency might have a dashboard showing high ingestion rates while simultaneously failing to provide the specific identity fields or historical context required to stop an active intrusion.
The real shift in the LRA is the expectation that logging must be treated as an executable system rather than a static document. When a system is executable, its health and compliance status are not inferred from spreadsheets or manual reviews. Instead, the system proves its own efficacy through continuous, automated validation. If an organization cannot programmatically verify that a specific event type is being parsed correctly, searchable within defined latency thresholds, and preserved according to policy, then the compliance document is functionally hollow.
Moving Beyond Passive Ingestion
Passive ingestion is the primary failure mode of traditional logging. Simply connecting a source to a Security Information and Event Management (SIEM) tool is not equivalent to achieving visibility. The telemetry pipe is often blind to the quality of the data it carries. A parser might update, causing the loss of critical fields, or a source system might misconfigure its own logging level, resulting in high-volume but low-value noise.
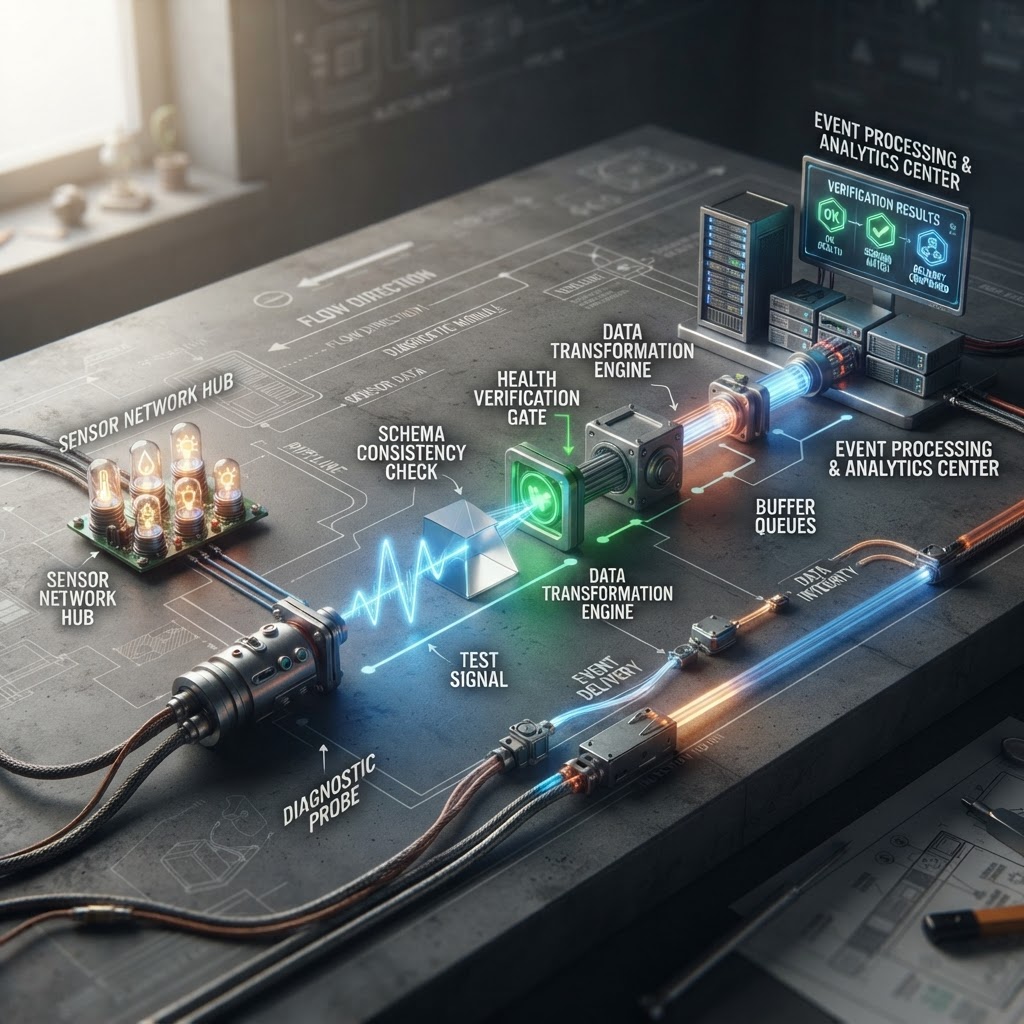
To move toward a high-fidelity architecture, agencies must implement negative testing and synthetic validation. This involves injecting known, controlled events into the pipeline to verify that they traverse every stage of the lifecycle. If an event is generated at the edge, does it reach the indexer with the same schema? Is the timestamp accurate? Are the required metadata fields preserved? These are engineering questions, not policy questions. By treating the logging infrastructure like a distributed application, agencies can gain early warnings of drift before a security incident exposes a total lack of observability.
Designing for Searchability over Retrievability
Data retention and data searchability are often conflated in compliance requirements. Agencies are frequently required to store data for significant durations, leading to the use of cold storage or archival tiers. While these tiers satisfy the letter of the law, they fail the needs of an incident responder. During a breach, the time required to rehydrate or restore logs from archive can be the difference between containment and catastrophe.
Modern logging architecture must decouple physical storage from search availability. By utilizing object-storage-backed search architectures, organizations can keep data in a state where it is queryable without maintaining every byte on expensive, high-performance NVMe storage. The objective is to ensure that six-month-old data is as accessible to a search query as yesterday's data. If the architecture cannot support this, it is effectively just a data warehouse for compliance, not a security asset.
Policy Centralization as a Technical Layer
In many decentralized environments, telemetry policy is applied inconsistently. One department might redact user PII, while another leaves it exposed. One team might enrich logs with geolocation data, while another relies on raw, unparsed strings. This inconsistency makes it nearly impossible for centralized security operations centers to write effective detection logic.
Agencies must move toward a unified policy enforcement layer. This is not about forcing a single massive SIEM upon every department. Instead, it is about creating a standard processing pipeline where redaction, classification, and enrichment occur in a predictable, auditable manner before the data reaches the storage tier. This ensures that when an investigator pulls a record, they can trust its structure regardless of where in the agency the data originated.
The AI Frontier and Telemetry Integrity
As federal agencies integrate LLMs and automated agents into their workflows, the logging requirement expands significantly. Agentic workflows generate a new class of event: the decision-making process. We must now log prompts, retrieved context, tool invocations, and internal reasoning. If this telemetry is missing or broken, the agency is effectively flying blind while deploying autonomous systems.
Furthermore, AI is not a replacement for fundamental telemetry. A sophisticated machine learning model for anomaly detection cannot overcome the absence of clean data. If the source system is not outputting consistent telemetry, no amount of AI-driven analysis will yield actionable insights. The maturity of the logging architecture is the ceiling for the effectiveness of any AI or automation layer built on top of it.
Final Argument
Federal agencies must abandon the notion that a logging plan is a piece of paper. The plan is the set of automated tests, the validation logic, and the observability metrics that prove the system is performing its duties. When validation becomes an integral part of operations, compliance becomes an inevitable byproduct of running the system correctly. Organizations that shift their focus from mere collection to continuous proof of telemetry integrity will be the only ones truly prepared for the modern threat landscape.